Technology Security Best Practices is an architecture decision with an owner and a rollback. On the technology security best practices for startups page, Technology Security Best Practices becomes a one-page file a tired operator can update: the rule, the owner, the dated review, and the kill condition. Public statistics appear only when they measure Technology Security Best Practices; otherwise the chart inventories this page's own file.
Retire the slogan around Technology Security Best Practices
Teams usually inherit a sentence about Technology Security Best Practices that sounded finished in a meeting and then died in the tools. Retire the slogan around Technology Security Best Practices.
Technology Security Best Practices needs one owner on the Technology Security Best Practices memo; a committee holds nothing when the launch slips.
Technology Security Best Practices leaves this page with one dated action, or it is still a wish.
Technology Security Best Practices is useful only when the Technology Security Best Practices memo can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for Retire the slogan around Technology Security Best Practices.
Technology Security Best Practices is finished when a tired person can update the file without a meeting.
What a current source actually measures
The expensive version of Technology Security Best Practices is the one that only works when the founder is in the room. What a current source actually measures.
Technology Security Best Practices stays short in the Technology Security Best Practices calendar so the same week the number moves the page moves.
Technology Security Best Practices still has a slice you can finish without a new budget line.
Technology Security Best Practices is useful only when the Technology Security Best Practices calendar can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for What a current source actually measures.
The working file for Technology Security Best Practices
If Technology Security Best Practices cannot survive a missed week, it was never an operating system. The working file for Technology Security Best Practices.
Technology Security Best Practices pairs every metric with the action it licenses, or the number is decoration.
Technology Security Best Practices goes to the board as the Technology Security Best Practices scorecard, not as a redesign.
Technology Security Best Practices is useful only when the Technology Security Best Practices scorecard can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for The working file for Technology Security Best Practices.
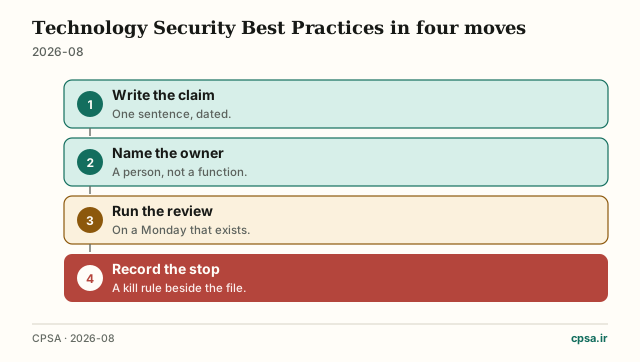
- Technology Security rule1 count
- Technology Security owne1 count
- Technology Security revi1 count
- Technology Security stop1 count
CPSA (2026-08). Inventory of the Technology Security Best Practices operating file. Desk count, not a census.
Moves you can finish this month
A borrowed playbook for Technology Security Best Practices fails the first time the jurisdiction, the cash, or the customer set changes. Moves you can finish this month.
Technology Security Best Practices refuses any tool that cannot export the Technology Security Best Practices folder if the vendor disappears.
Technology Security Best Practices that ships this Friday beats a doctrine that waits for a retreat.
Technology Security Best Practices is useful only when the Technology Security Best Practices folder can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for Moves you can finish this month.
| Move | Owner | Done when |
|---|---|---|
| Open the Technology Security Best Practices file | Founder | A titled one-pager exists |
| Name the owner | CEO | A person is written on page one |
| Date the next review | Ops | A Monday is on the calendar |
The failure mode this topic hides
Technology Security Best Practices gets treated as a branding exercise precisely when the file should have an owner. The failure mode this topic hides.
Technology Security Best Practices is reviewed on a Monday that already exists, never on a new ceremony.
Technology Security Best Practices leaves this page with one dated action, or it is still a wish.
Technology Security Best Practices is useful only when the Technology Security Best Practices brief can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for The failure mode this topic hides.
When the usual rule should not apply
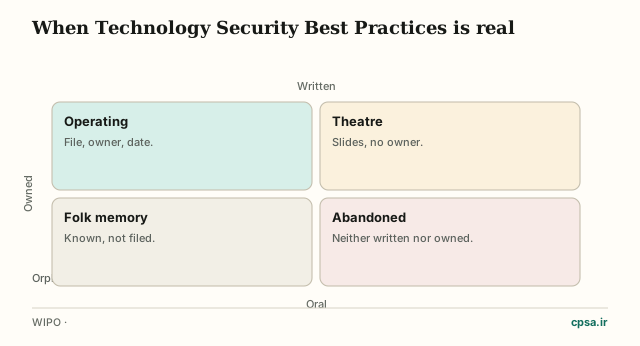
Most arguments about Technology Security Best Practices are arguments about whose calendar the next action sits on. When the usual rule should not apply.
Technology Security Best Practices becomes one sentence a new hire can repeat, or the culture is still oral.
Technology Security Best Practices still has a slice you can finish without a new budget line.
Technology Security Best Practices is useful only when the Technology Security Best Practices memo can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for When the usual rule should not apply.
The Monday instrument
You do not need a new platform to start Technology Security Best Practices; you need a named artifact and a dated review. The Monday instrument.
Technology Security Best Practices records a kill rule beside the Technology Security Best Practices calendar, because a file that cannot stop is ignored.
Technology Security Best Practices goes to the board as the Technology Security Best Practices calendar, not as a redesign.
Technology Security Best Practices is useful only when the Technology Security Best Practices calendar can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for The Monday instrument.
Write the one-sentence rule for Technology Security Best Practices.
Put an owner and a review date on the same page.
Attach the source for any number you keep.
Show the page in the next staff meeting.
A decision you can write in one sentence
The tell that Technology Security Best Practices is theatre is a dashboard nobody can update without a workshop. A decision you can write in one sentence.
Technology Security Best Practices links to cash, counsel, or customer so it cannot float as a slogan.
Technology Security Best Practices that ships this Friday beats a doctrine that waits for a retreat.
Technology Security Best Practices is useful only when the Technology Security Best Practices scorecard can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for A decision you can write in one sentence.
Where this sits in the rest of the company
Technology Security Best Practices is downstream of cash and trust. Ignore either and the ritual becomes costume. Where this sits in the rest of the company.
Technology Security Best Practices shrinks the test when two reviews miss the written rule, instead of adding a slide.
Technology Security Best Practices leaves this page with one dated action, or it is still a wish.
Technology Security Best Practices is useful only when the Technology Security Best Practices folder can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for Where this sits in the rest of the company.
Close the loop before the month ends
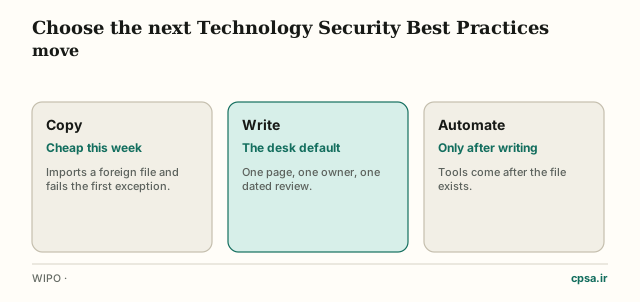
Close Technology Security Best Practices the way you close a ticket: acceptance criteria, owner, and a time the work is allowed to stop. Close the loop before the month ends.
Technology Security Best Practices keeps its next reversible test in the Technology Security Best Practices brief, with the source date beside the claim.
Technology Security Best Practices still has a slice you can finish without a new budget line.
Technology Security Best Practices is useful only when the Technology Security Best Practices brief can be opened in under two minutes, updated without a meeting, and shown to a new hire who was not in the last argument. That is the standard this page uses for Close the loop before the month ends.
Technology Security Best Practices is finished when a tired person can update the file without a meeting.
Frequently asked questions
When should Technology Security Best Practices start?
Technology Security Best Practices should start the week two people will be judged by the same file. A private note can wait.
What is the smallest useful Technology Security Best Practices version?
Technology Security Best Practices fits on one page: the rule, the owner, the next review date, and the kill condition.
Which Technology Security Best Practices number belongs on a board slide?
Technology Security Best Practices may show a board number only when the figure is sourced and dated; otherwise show the file.
What if the first Technology Security Best Practices review is missed?
Technology Security Best Practices shrinks to the week you actually have. Adding software after a missed review is how the file dies.
Who owns Technology Security Best Practices when functions disagree?
Technology Security Best Practices has one named person. A rotating committee turns the work into an agenda item that vanishes.
How does Technology Security Best Practices change after a priced round?
Technology Security Best Practices keeps the same file and grows an audience. Rewrite page one so a new director needs no tour.
Answers to the questions this topic usually leaves hanging.
How we sourced this
Sources for Technology Security Best Practices are listed below. A number without a date and a publisher does not belong on this page.
- WIPOBackdrop source for this cluster.
- OECDCross-country operating context.
- BLS BEDYoung-firm backdrop, used only when relevant.
- Carta private marketsUS private-market calendar used as dating context.
- CPSA deskOperating file for Technology Security Best Practices.
Primary sources used for this edition.
The bottom line
Treat Technology Security Best Practices as a file you can update on a tired Monday. If the page still needs a tour, it is not done.
If you want the adjacent decisions next, start with Technology Stack Selection Criteria for Startups, Technology Team Building and Management, Global Startup Market Share, Technology Project Management Methodologies.